Tagged Third Party Risk.
Every article we've tagged with "Third Party Risk".
From the team.
 Risk Management
VRM is key to managing and monitoring third-party vendors products and services
Vendor Risk Management (VRM) is critical for identifying, managing, and monitoring third-party risks that could compromise an organisation’s cybersecurity, financial stability, and reputation. As outsourcing grows, continuous audits and information security reviews across the entire vendor lifecycle — from qualification to relationship termination — are essential. RiskXchange offers a robust VRM framework that helps businesses reduce third-party risks and maintain strong compliance across multiple vendors and jurisdictions.
Read more Cybersecurity
How to Measure Cybersecurity Risk: A Strategic Guide for 2026
Learn how to measure cybersecurity risk with our 2026 guide. Ditch subjective heat maps for data-driven models that quantify threats in real financial terms.
Read more Cybersecurity
How to define sensitive data and the means of protecting it
Understanding and protecting sensitive data is essential in today’s threat landscape, where breaches increasingly target personal and confidential information. This guide outlines how to define sensitive data using the CIA triad—confidentiality, integrity, and availability—and highlights security measures like encryption, access controls, and vendor risk management. With third-party vulnerabilities rising, organisations must classify, monitor, and safeguard sensitive information—especially in cloud environments—to maintain compliance and prevent costly data breaches.
Read more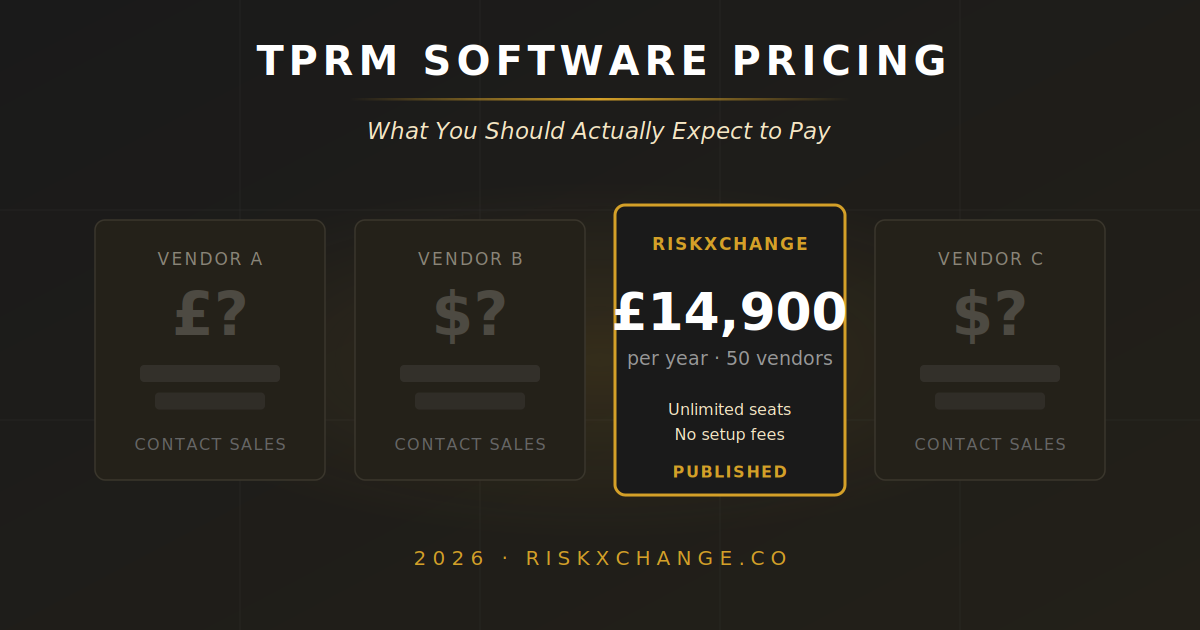 Risk Management
TPRM Software Pricing: What You Should Actually Expect to Pay in 2026
Almost every TPRM vendor hides its pricing. Here's what buyers actually pay in 2026 — real benchmark figures for SecurityScorecard, Bitsight, UpGuard and others, the hidden cost traps to negotiate away, and RiskXchange's published prices in full.
Read more Risk Management
Third Party Risk Management in the context of GDPR
Third-party risk management is essential for maintaining GDPR compliance. Organisations must ensure vendors handle personal data securely through due diligence, risk assessments, contract controls, and continuous compliance monitoring. Key focus areas include data minimisation, access limitations, and third-party audit rights. Real-world breaches, like the Target incident, show how weak vendor controls can expose sensitive data. RiskXchange supports businesses by providing instant cyber risk ratings and helping maintain GDPR-aligned third-party assurance.
Read more Risk Management
Ensuring your organisation has superior cybersecurity monitoring is paramount today
Cybercrime is accelerating, and continuous cybersecurity monitoring is essential for real-time threat detection and risk mitigation. As attack surfaces expand with remote work and third-party vendors, organisations must adopt advanced monitoring practices to protect critical data. RiskXchange offers end-to-end visibility, compliance verification, and proactive security solutions that help businesses stay ahead of evolving cyber threats.
Read more