The thinking behind The Agency.
Insights and analysis on third-party risk management, vendor security, regulatory compliance, and the agentic shift reshaping how TPRM teams actually work.
From the team.
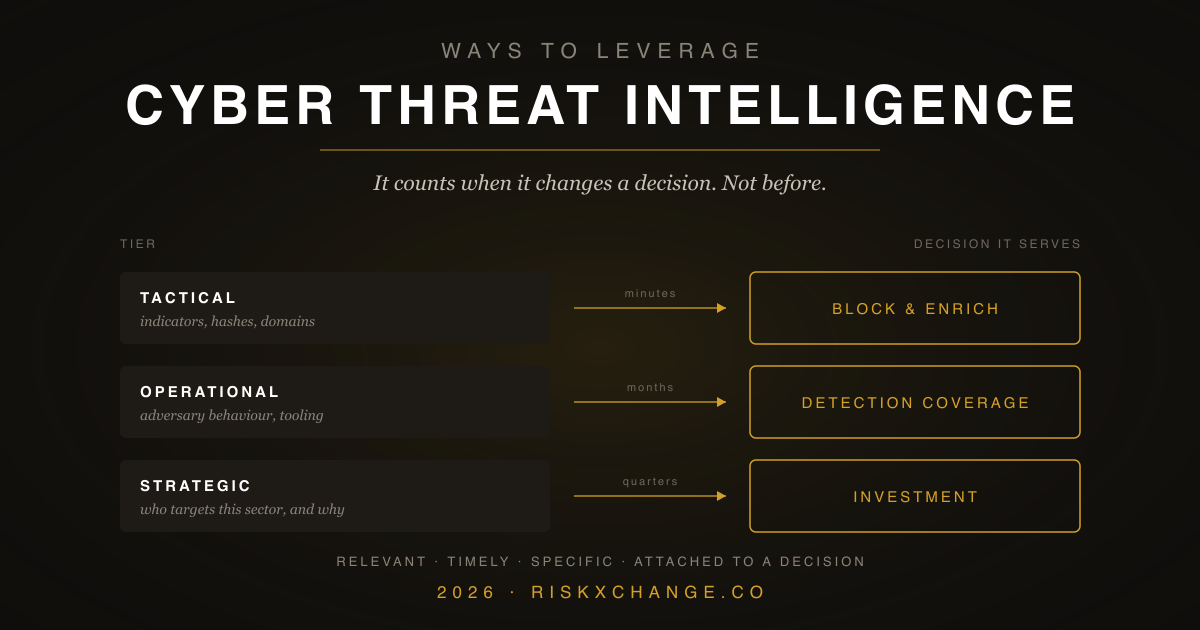
Ways to Leverage Cyber Threat Intelligence
Most organisations have threat intelligence. Far fewer can name a decision made differently because of it. Practical ways to close that gap.
Read more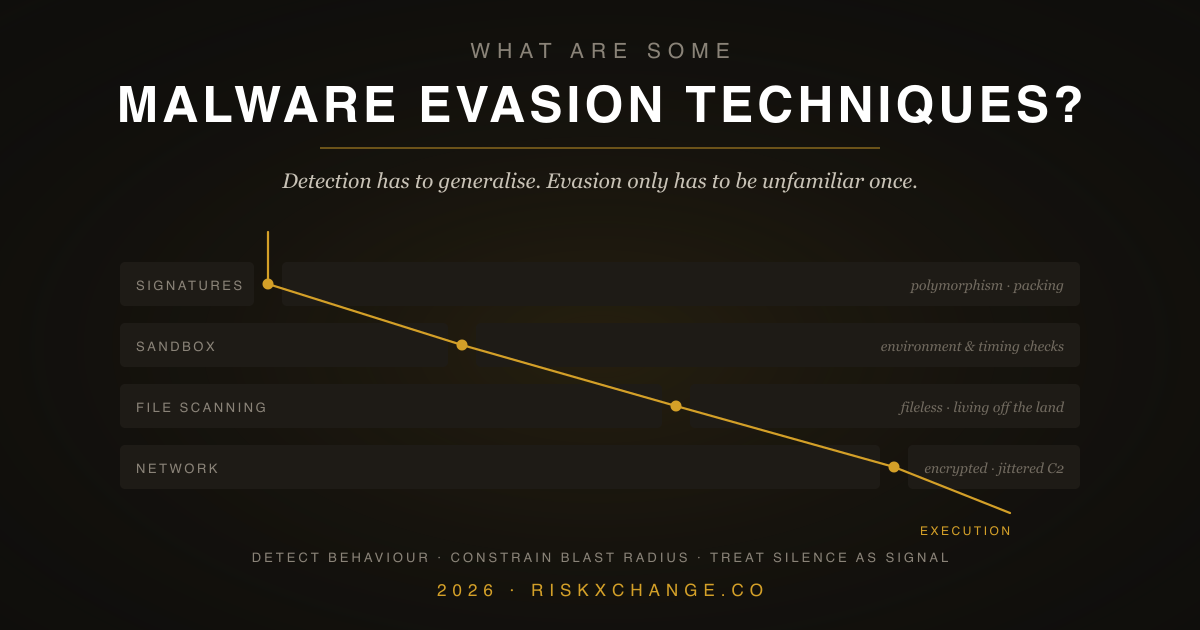
What Are Some Malware Evasion Techniques?
Detection has to generalise; evasion only has to be unfamiliar once. A look at how malware avoids signatures, sandboxes and network monitoring, and which defences survive contact.
Read more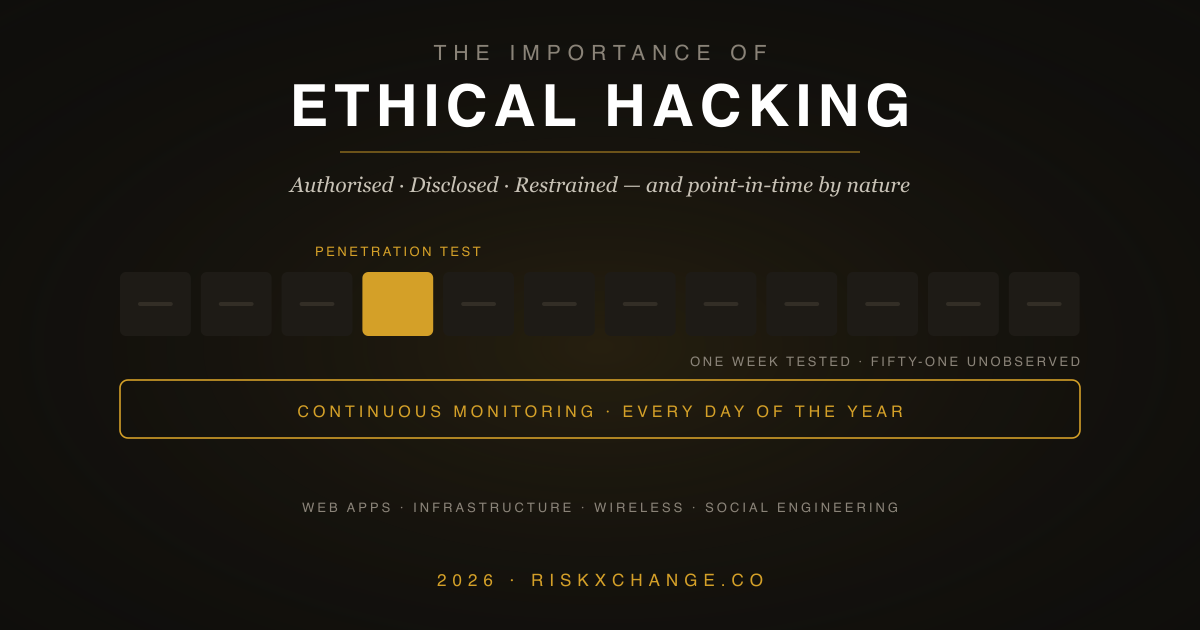
The Importance of Ethical Hacking: Maintaining Integrity in Cyber Security
Ethical hacking borrows the attacker's method to close the defender's asymmetry. What it covers, who is qualified to do it, and the limitation every point-in-time test shares.
Read more Risk Management
'Critical Supplier' Under the Cyber Security and Resilience Bill: Are You One, and What Happens Next?
The Cyber Security and Resilience Bill lets regulators designate individual suppliers as 'critical' — pulling them directly into scope even if they'd otherwise be unregulated. Here's what designation means, whether it could apply to you, and what suppliers and their customers should do now.
Read more Risk Management
The Cyber Security and Resilience Bill: What It Means for Your Suppliers
The UK's Cyber Security and Resilience Bill has reached committee stage in the Lords — and for the first time, it brings your suppliers and managed service providers directly into scope. Here's what security and procurement leaders need to do now.
Read more Risk Management
DORA Register of Information: A Complete Template and Walkthrough
The DORA Register of Information is the most data-intensive obligation in the framework: 15 interlinked templates, xBRL-CSV format, and validation that gets stricter every cycle. A complete walkthrough — structure, deadlines, the failure modes from two reporting rounds, and how to build a register that passes.
Read moreStop reading. Start running TPRM differently.
Book a 30-minute call and we'll have NOVA, ARIA and REX produce a complete posture report on a vendor of your choice inside 24 hours.