Tagged Third Party Risk.
Every article we've tagged with "Third Party Risk".
From the team.
 Risk Management
What Is a Security Rating Score? A Comprehensive Guide for 2026
Learn what a security rating score is and why it has become a critical benchmark for digital trust and resilience in 2026. Discover how AI-native platforms analyse external risk signals, quantify cybersecurity posture, and help organisations strengthen third-party risk management, improve board reporting, and maintain continuous visibility across their entire digital attack surface.
Read more Compliance
GDPR compliance checklist for 2022
A clear and practical GDPR compliance checklist for 2022 helps organisations align with EU data protection laws. Key areas include mapping data collection, appointing a Data Protection Officer, reporting breaches, updating privacy policies, and managing third-party risks. The guide also explains the roles of data controllers and processors. RiskXchange supports businesses with automated tools to streamline GDPR compliance and monitor supplier risks.
Read more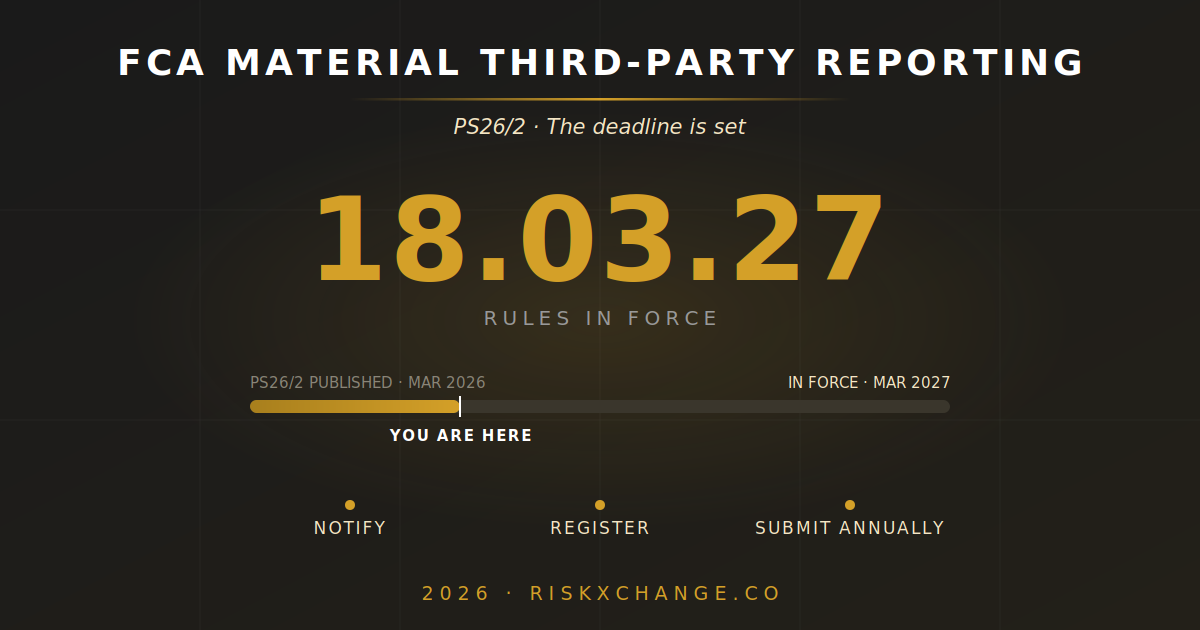 Risk Management
FCA Material Third-Party Reporting: Preparing for the March 2027 Deadline
The FCA's material third-party reporting rules under PS26/2 come into force on 18 March 2027. Here's who's in scope, what counts as "material", what the register demands, and a month-by-month preparation plan that starts now.
Read more Risk Management
The Comprehensive Vendor Risk Assessment Checklist for 2026
A modern vendor risk assessment checklist for 2026 goes beyond static questionnaires to deliver continuous, data-driven visibility into your third-party ecosystem. This guide outlines how to replace manual processes with real-time monitoring, tier vendors effectively, and use cybersecurity ratings to reduce supply chain risk and strengthen operational resilience.
Read more Risk Management
The Financial Impact of Supply Chain Attacks in 2026: A Strategic Analysis
The financial impact of supply chain attacks in 2026 extends far beyond immediate breach recovery costs. This strategic analysis explores how AI-driven threats, fourth-party vulnerabilities, and evolving regulations like DORA are reshaping enterprise risk. Learn how to quantify hidden financial exposure, reduce operational disruption, and strengthen resilience through continuous, AI-native third-party risk management.
Read more Risk Management
The Cascading Consequences of Poor Vendor Security: An Enterprise Guide for 2026
Poor vendor security can lead to costly data breaches, operational disruption, regulatory penalties, and lasting reputational damage. Discover the key consequences of third-party security failures in 2026 and learn how continuous monitoring, real-time risk intelligence, and AI-driven vendor risk management can help organisations strengthen supply chain resilience and maintain stakeholder trust.
Read more