Category: Compliance.
Every article we've published under "Compliance".
From the team.
 Compliance
The Essentials of Modern Cybersecurity Law: A 2026 Regulatory Guide
Cybersecurity law in 2026 has shifted from voluntary frameworks to enforceable mandates that demand continuous, real-time oversight. This guide breaks down global regulations like NIS2, DORA, and CIRCIA, and shows how to move from static compliance to a legally defensible, data-driven security posture across your entire supply chain.
Read more Risk Management
Cyber Risk Appetite Statement Examples: A Guide for CISOs in 2026
A cyber risk appetite statement is no longer a static compliance document—it’s a strategic control mechanism for defining how much digital risk an organisation is willing to accept in pursuit of its goals. In 2026, with tightening regulations like SEC four-day disclosure rules and frameworks such as NIS2 and DORA, CISOs and boards must translate risk into clear, quantifiable boundaries that align security decisions with business outcomes. This guide explores how to build and operationalise a modern cyber risk appetite statement, complete with real-world examples across financial services, technology, and critical infrastructure, and shows how continuous risk intelligence and AI-native monitoring help keep those boundaries enforceable in real time.
Read more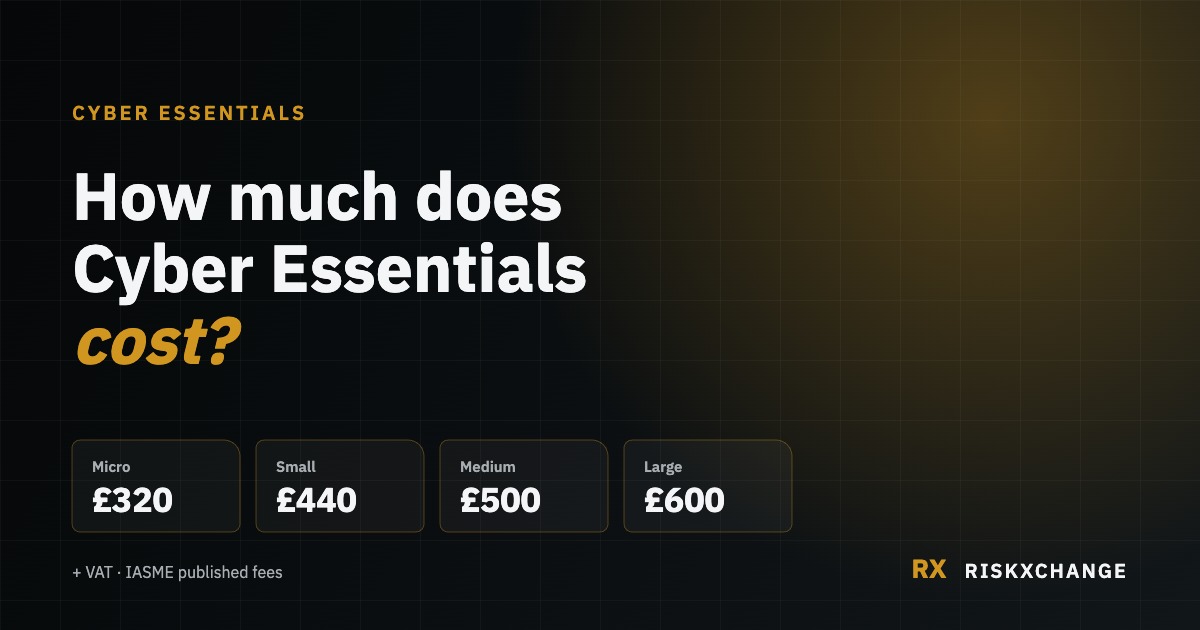 Compliance
How much does Cyber Essentials cost?
The published IASME assessment fees for every organisation size, what Cyber Essentials Plus actually costs, what renewal costs, and the costs that never appear on the price list.
Read more Risk Management
Third-Party Attack Surface Discovery: Securing the Extended Enterprise
Third-party attack surface discovery gives enterprises real-time visibility into the hidden vulnerabilities across their vendor ecosystem. By moving beyond static questionnaires and leveraging AI-native continuous monitoring, organizations can identify shadow IT, map fourth-party dependencies, and establish quantifiable security ratings for every partner. This guide explains how discovery-led TPRM helps security teams reduce supply chain risk, improve remediation workflows, and meet evolving compliance demands such as DORA and NIS2 with confidence.
Read more Risk Management
ESG Risk Management: A Strategic Framework for Supply Chain Resilience in 2026
ESG risk management in 2026 requires a shift from static reporting to continuous, AI-driven monitoring that provides real-time visibility across the entire supply chain. By integrating environmental, social, and governance metrics with cybersecurity ratings, organisations can eliminate blind spots, automate compliance, and transform ESG from a reporting obligation into a measurable driver of resilience and strategic advantage.
Read more Risk Management
Automated Vendor Risk Management: The 2026 Strategic Guide
Manual vendor oversight can no longer keep up with today’s fast-moving supply chain risks, especially as organisations manage hundreds of third parties with limited resources. This guide explains how automated vendor risk management replaces static questionnaires with continuous, AI-driven intelligence, giving security teams real-time visibility into vendor posture, faster remediation cycles, and measurable risk reduction. It explores how automation, security ratings, and integrated monitoring help organisations move from reactive assessment to proactive control across the entire vendor ecosystem.
Read more